Meta Bolsters Muse Safety Warning After Security Vulnerability Found: Report
Meta has moved to strengthen safety warnings around its Muse AI image, generation feature after an external security researcher identified a vulnerability that could have exposed user data, according to reports. The flaw was reportedly submitted through Meta's bug bounty program, a channel that pays independent researchers for responsibly disclosing security gaps before they can be exploited. The issue had not been publicly disclosed before the company acted on it, and it is understood to have affected the way Muse handled certain user interactions. Meta has not issued a detailed public statement outlining the precise technical nature of the vulnerability, and the company has historically declined to comment on specific bug bounty submissions. The development matters because Muse sits at the centre of Meta's push to embed generative artificial intelligence across its family of apps, including Facebook, Instagram and WhatsApp.
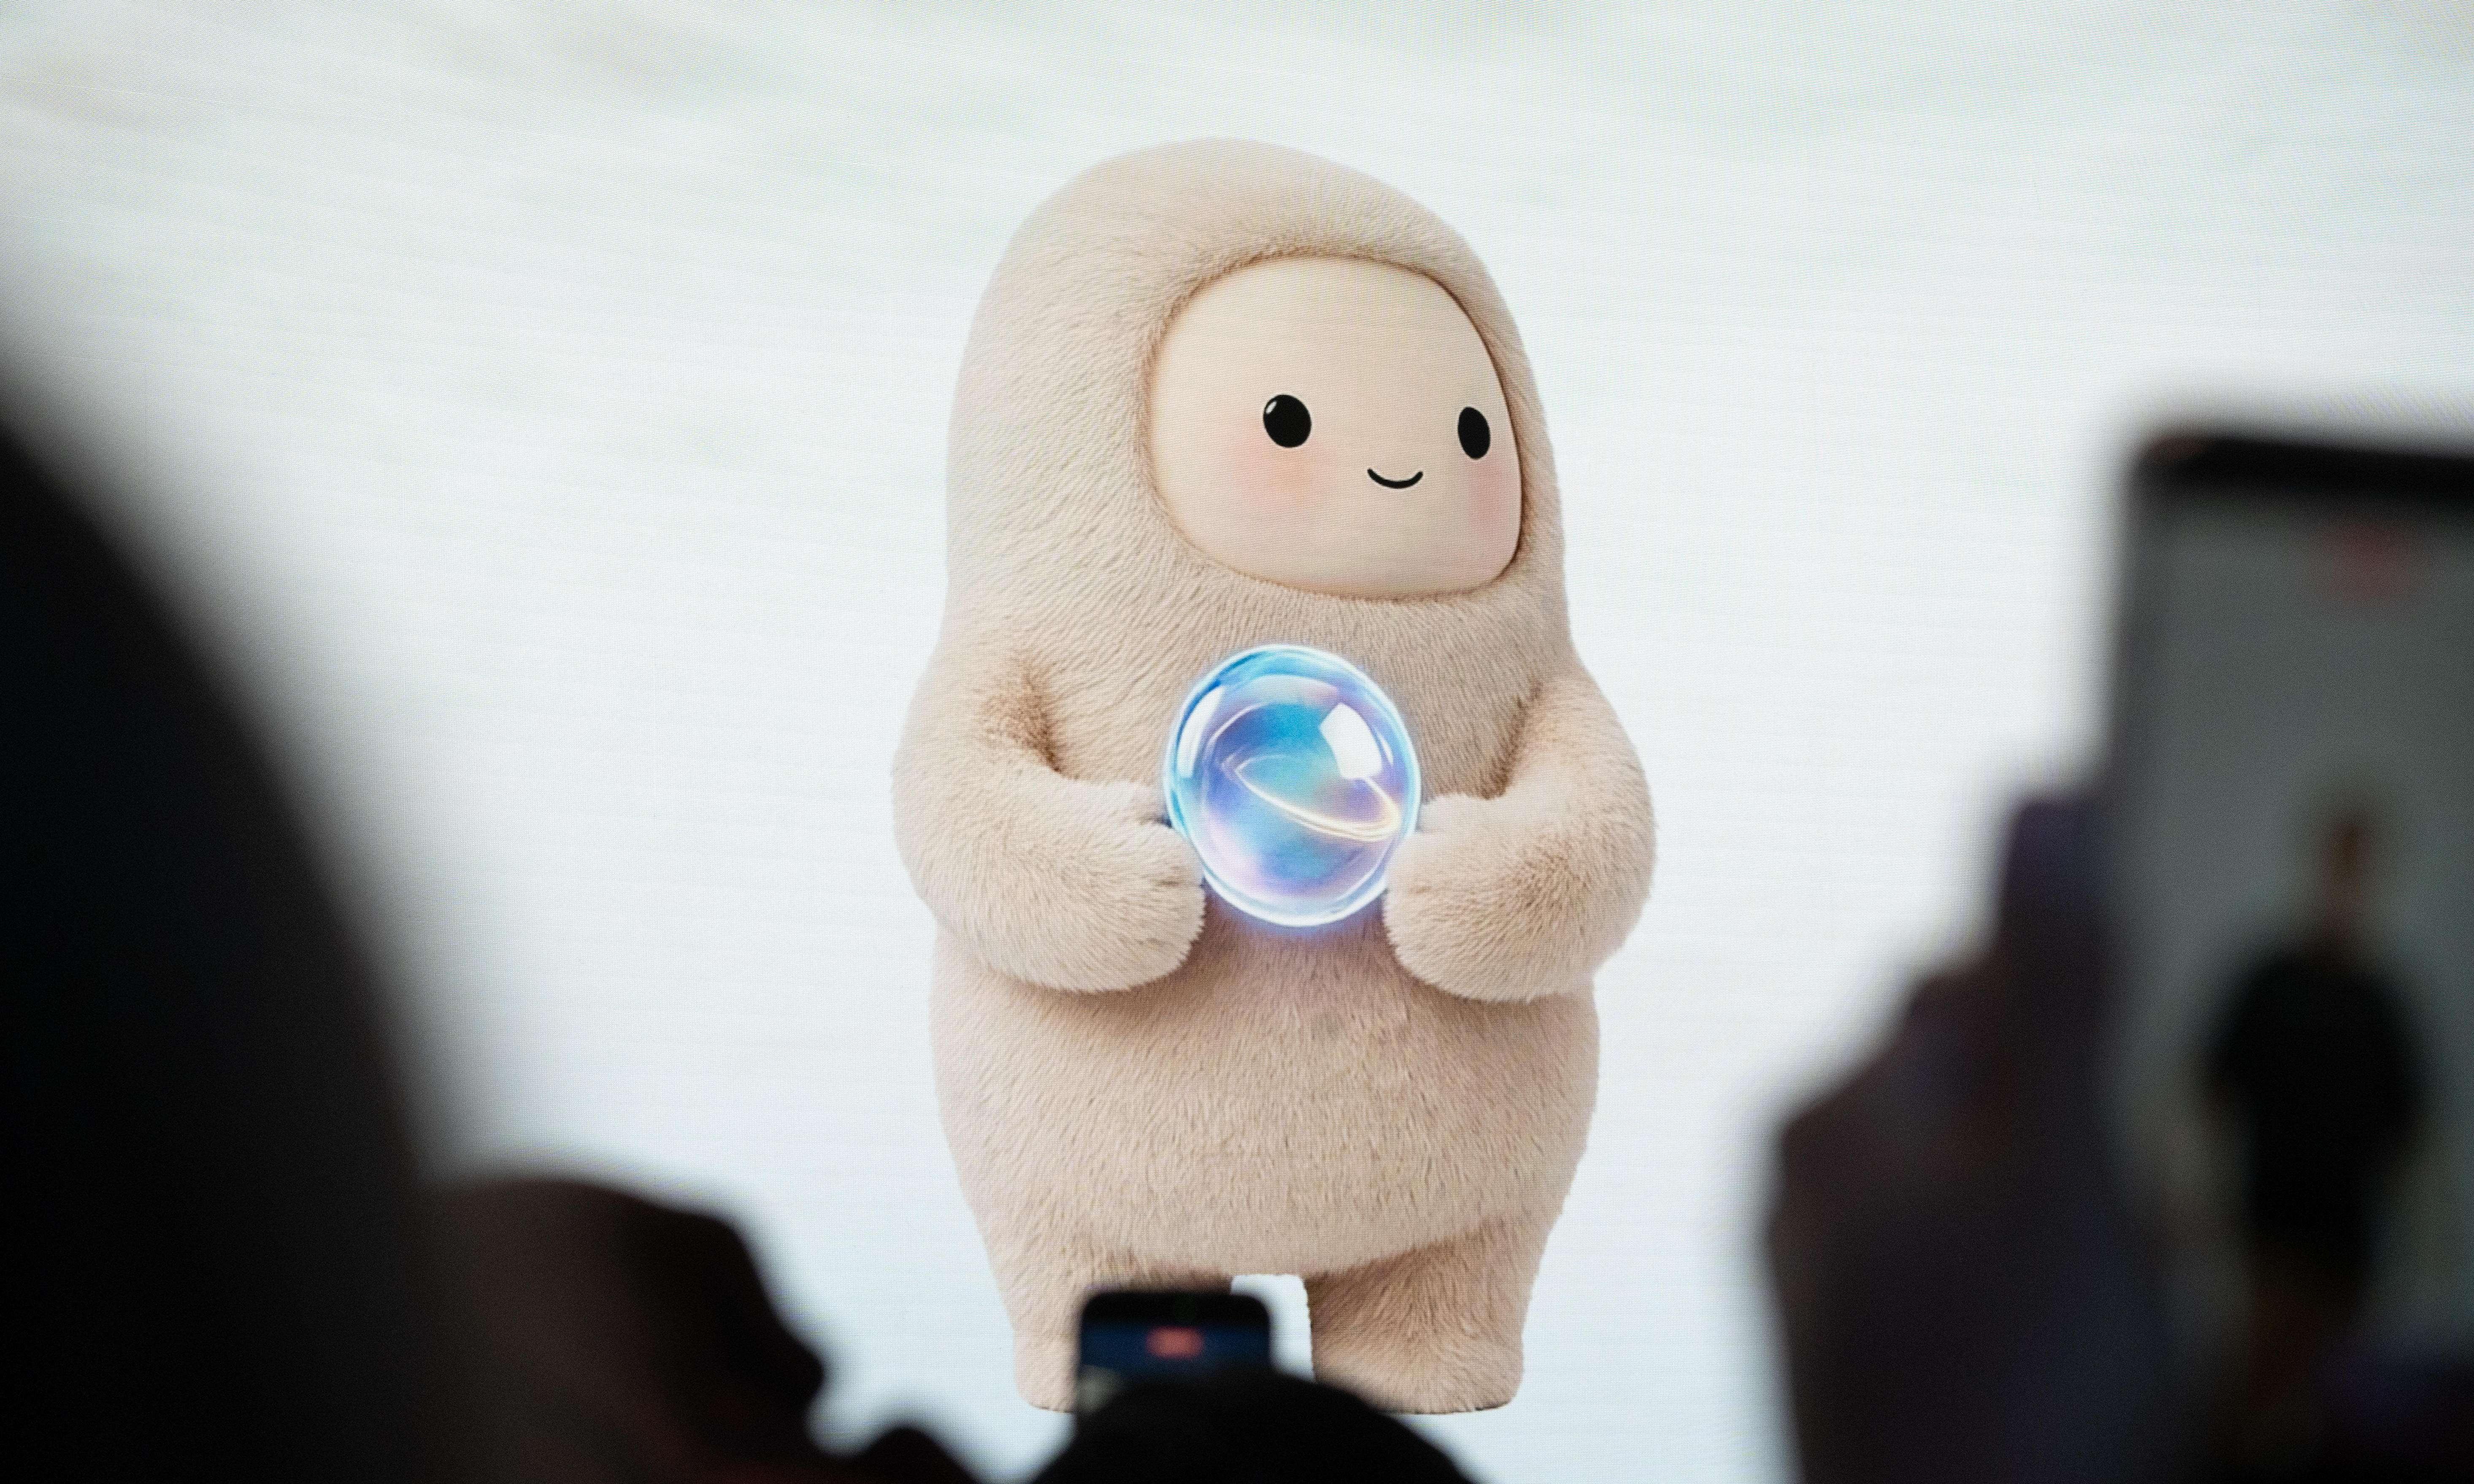
Muse is the branding Meta has attached to its generative AI efforts, spanning tools that let users create images and other content through simple text prompts. The feature has been rolled out gradually across Meta's platforms, reflecting the company's ambition to compete with rivals such as OpenAI, Google and others in the crowded generative AI market. Bug bounty programs have become a standard part of the security infrastructure at major technology firms, allowing outside researchers to probe systems for weaknesses in exchange for financial rewards and recognition. Meta has operated such a program for years and has paid out substantial sums to researchers who uncover serious flaws. The reported Muse issue fits a familiar pattern in which AI products, launched at speed, are scrutinised by the security community soon after release.
Details of the vulnerability remain limited, and much of what is known rests on the outside researcher's account rather than official confirmation from Meta. Reports indicate the flaw could have allowed an attacker to gain access to a user's information under certain conditions, though the exact mechanism has not been publicly detailed. Meta is said to have addressed the issue after being notified, in line with how responsible disclosure typically works. The company has not confirmed the identity of the researcher or the size of any bounty payout, and such details are usually kept confidential under the terms of bug bounty arrangements. What is clear is that the warning system around Muse has been reinforced, suggesting Meta has adjusted how it flags or communicates risks tied to the feature.
The disclosure is likely to intensify scrutiny of how AI features are secured before and after they reach millions of users. Security researchers have repeatedly warned that generative AI tools introduce new categories of risk, from data leakage to prompt manipulation, that traditional software testing may not fully capture. Consumer advocacy groups and privacy watchdogs in India and elsewhere have been pressing platforms to be more transparent about how AI systems handle personal data. Meta's handling of the Muse flaw will be watched as a test of whether its bug bounty pipeline can keep pace with the rapid deployment of AI products. Any perception that user data was at risk could damage trust at a time when regulators are already examining the company's practices.
The episode comes amid a broader global push to regulate artificial intelligence and hold platforms accountable for security failures. India has been developing its own approach to AI governance, with debates over data protection, deepfake regulation and platform liability unfolding alongside the country's large user base on Meta's apps. Regulators in the European Union and the United States have similarly stepped up oversight of AI systems, particularly those that process personal information. Bug bounty disclosures, while often low, profile, feed into this wider conversation about whether companies are doing enough to protect users. Meta's decision to bolster warnings around Muse reflects the balancing act platforms face between shipping features quickly and securing them adequately.
Meta has weathered similar episodes before, including past bug bounty disclosures involving Instagram, WhatsApp and its advertising systems, where researchers found flaws that the company later patched. The Cambridge Analytica scandal remains the most prominent example of how data, related vulnerabilities can escalate into a full, blown reputational and political crisis. More recently, AI, specific concerns have surfaced across the industry, with researchers demonstrating ways to extract training data or bypass safety guardrails in various models. These precedents suggest that individual bug reports, even when resolved quietly, contribute to a cumulative picture of a company's security posture. Meta has generally emphasised that it investigates and fixes reported issues promptly.
Going forward, Meta is expected to continue refining safeguards around Muse and to keep engaging with researchers through its bug bounty program. The company may face questions from regulators and lawmakers about the timeline of the disclosure and the nature of the fix, particularly if further details emerge. Users are unlikely to see dramatic changes, but the incident could prompt more transparency about how AI features are tested before launch. The security research community will likely continue probing Muse and other Meta AI tools for weaknesses. How Meta communicates about such fixes, and whether it publicly acknowledges the flaw, could shape the narrative around its commitment to safety in the AI era.